Blog

  • autocomplete az commands in zsh on a mac

    the following script assumes that you have the az command installed on your mac. if you have installed it using homebrew then it copies the auto-completion file to the location /opt/homebrew/etc/bash_completion.d/az already. all we have to do is to make it auto load on zsh startup. copy and paste the following command to do it. restart your zsh (cmd+q) after entering this command.

    [[ -f /opt/homebrew/etc/bash_completion.d/az ]] && echo -e '\n# azure cli auto completion\nautoload -U +X bashcompinit && bashcompinit\nsource /opt/homebrew/etc/bash_completion.d/az' >> ~/.zshrc || echo 'autocomplete file not found'
  • until … done loop in gnu/bash

    bash has three types of loop constructs
    – for
    – while
    – until

    until loop is used to iterate over the body of the loop till the condition stays false.

    syntax:

    until [ condition ];
    do
    block-of-statements
    done

    example:

    #!/bin/bash
    echo “example of until”
    i=20
    until [ $i == 1 ]; do  # condition stays false
      echo "${i} is still greater than 1”
      i=$((i-1))  # i = i - 1
    done
    echo “value of i = ${i}"

    You may chose to throw this code in a shell script and see it go.

  • configure docker host with remote api on your linux machine

    step 1: install docker engine. follow steps for your os from the docker documentation here – https://docs.docker.com/engine/install/

    step 2: assuming that you’re using ubuntu, open the file docker.service located at the path /lib/systemd/system/docker.service

    step 3: search for the line which says ExecStart. by default it should have something like this ExecStart=/usr/bin/dockerd -H fd:// --containerd=/run/containerd/containerd.sock . add the argument -H tcp://0.0.0.0:2376 to the dockerd command. the final command should look like this `ExecStart=/usr/bin/dockerd -H fd:// -H tcp://0.0.0.0:2376 --containerd=/run/containerd/containerd.sock

    step 4: we need to reload the systemd daemon and restart the docker service. use the command systemctl daemon-reload && systemctl restart docker.service to achieve this.

    step 5: test the change. run curl -s http://<ip_address_of_host>:2376 this should spit out the json message showing docker versions. if this doesnt work, make sure the firewall allows you to connect to this port.

  • swap file appears to have holes

    error message –

    root@host:~# swapon /swap-file-00
    swapon: /swap-file-00: skipping - it appears to have holes.

    solution – you need to zero-fill the file you are using as swap

    steps to remediate this –

    first of all, remove the existing file with the holes.

    root@host:~# rm /swap-file-00

    create the new swap file using the following command:

    root@host:~# dd if=/dev/zero of=/swap-file-00 bs=1M count=5120 status=progress
    5322571776 bytes (5.3 GB, 5.0 GiB) copied, 6 s, 887 MB/s
    5120+0 records in
    5120+0 records out
    5368709120 bytes (5.4 GB, 5.0 GiB) copied, 6.08009 s, 883 MB/s

    check the file type being displayed now. it’s just a data file.

    root@host:~# file /swap-file-00
    /swap-file-00: data

    if your system says something like the following, it just means that the file command is not installed on your system. you may either ignore the file commands in the further steps since they are not required in getting a swap file operational on your system. they are being used to verify the file contents based on their magic numbers. or you may chose to install the file command using the package manager on your gnu/linux, say apt -y install file on a debian/ubuntu:

    file: command not found

    change the permissions on it:

    root@host:~# chmod 600 /swap-file-00

    make the new file as swap file:

    root@host:~# mkswap /swap-file-00
    Setting up swapspace version 1, size = 5 GiB (5368705024 bytes)
    no label, UUID=738f253b-aed0-46ac-bc50-b4d1fe2d1702

    check the file type being displayed now. it’s a swap file.

    root@host:~# file /swap-file-00
    /swap-file-00: Linux/i386 swap file (new style), version 1 (4K pages), size 1310719 pages, no label, UUID=738f253b-aed0-46ac-bc50-b4d1fe2d1702

    turn on the swap, as usual

    root@host:~# swapon /swap-file-00

    check if it is being used as a swap file

    root@host:~# swapon --show
    NAME TYPE SIZE USED PRIO
    /swap-file-00 file 5G 0B -2
  • unexport/remove a variable in the shell

    say you have assigned some value to a variable from the shell or a shell script using the export command and now you want to remove that variable, either programatically or manually.

    (more…)
  • list all versions of an available package using yum/dnf

    dnf list <packagename> --showduplicates

    Example:

    [ec2-user@ip-172-31-39-90 ~]$ sudo dnf list kmod-kvdo --showduplicates
    
     Updating Subscription Management repositories.
     Unable to read consumer identity
     This system is not registered to Red Hat Subscription Management. You can use subscription-manager to register.
     Last metadata expiration check: 0:04:00 ago on Thu 03 Jun 2021 23:54:45 UTC.
     Available Packages
     kmod-kvdo.x86_64  6.2.0.293-50.el8  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.0.293-52.el8_0  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.0.293-53.el8_0  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.1.138-57.el8  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.1.138-58.el8_1  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.2.117-65.el8  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.3.114-74.el8  rhel-8-baseos-rhui-rpms
     kmod-kvdo.x86_64  6.2.4.26-77.el8  rhel-8-baseos-rhui-rpms
    
    [ec2-user@ip-172-31-39-90 ~]$
  • autofs mounts

    autofs is a nice traditional way to mount the nfs directories on-demand on the nfs clients. was originally used to mount the user home directories to the clients to make them sort of roaming user profiles, but this doesnt stop us from using it to configure nfs mounts in other ways. using autofs saves unnecessary resource allocation to mount the resources on a client machine, which may never be accessed in that session. it also saves the open handles on the nfs server, which is another plus.

    ps: the examples below have been done on a centos 8.3 gnu/linux machine. adjust the path locations accordingly as per your flavor of gnu/linux. rest of the options should be good.

    install autofs

    dnf -y install autofs

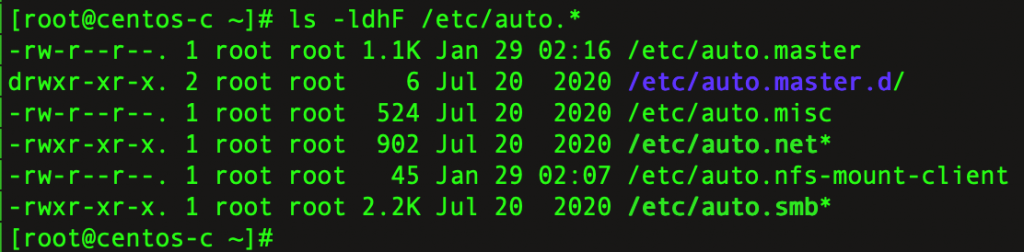
    define the mounts in the master configuration file named auto.master in /etc

    directory listing for auto.master in /etc in a CentOS 8.3 machine
    directory listing for auto.master in /etc in a CentOS 8.3 machine

    explanation with example

    nfs server ip: 139.59.88.183
    nfs export: /nfs-mount-00

    client ip: 139.59.94.153
    client directory where we need to mount the nfs share: /nfs-mount-client

    step 1: add the map file path in auto.master

    the text i added to the auto.master has been bolded for easy reading below

    [root@centos-c ~]# cat /etc/auto.master
     #
     # Sample auto.master file
     # This is a 'master' automounter map and it has the following format:
     # mount-point [map-type[,format]:]map [options]
     # For details of the format look at auto.master(5).
     #
     /misc   /etc/auto.misc
     /nfs-mount-client  /etc/auto.nfs-mount-client  --ghost
     #
     # NOTE: mounts done from a hosts map will be mounted with the
     # "nosuid" and "nodev" options unless the "suid" and "dev"
     # options are explicitly given.
     #
     /net    -hosts
     #
     # Include /etc/auto.master.d/*.autofs
     # The included files must conform to the format of this file.
     #
     +dir:/etc/auto.master.d
     #
     # If you have fedfs set up and the related binaries, either
     # built as part of autofs or installed from another package,
     # uncomment this line to use the fedfs program map to access
     # your fedfs mounts.
     #/nfs4  /usr/sbin/fedfs-map-nfs4 nobind
     #
     # Include central master map if it can be found using
     # nsswitch sources.
     #
     # Note that if there are entries for /net or /misc (as
     # above) in the included master map any keys that are the
     # same will not be seen as the first read key seen takes
     # precedence.
     #
     +auto.master
     [root@centos-c ~]#

    step 2: define the map file (added above)

    [root@centos-c ~]# cat /etc/auto.nfs-mount-client 
    data -fstype=nfs 139.59.88.183:/nfs-mount-00
    [root@centos-c ~]#

    step 3: reload the autofs daemon

    systemctl reload autofs.service

    that it! now when you browse to the mounted directory on the nfs client, the nfs will be mounted automatically.

    Good things to know

    • the default settings in autofs do not show the mounted directories. this might give you the illusion that the directory is not mounted at all even when you are in the mount point! you need to remember the name of the directory to cd into that. if you dont want to remember all this, then you may use the –ghost option in the map file options defined in the auto.master configuration file, as shown in the example above. i prefer that and like to see the mounted directories.
    • another way would be to turn on the browse_mode in the autofs.conf file. it is the same as adding the –ghost option manually.
    • if you’re using a systemd based linux, you might not be interested in autofs at all! yeah, use the systemd automount instead. it is built in to the system already and no more remembering the autofs mapping and stuff. no installing the additional autofs package either.

    References

    man 5 autofs

  • selinux prevents mounted directories for serving content for httpd

    error message

    (13)Permission denied: [client <ipaddress>:<port>] AH00035: access to /index.html denied (filesystem path '/opt/rh/httpd24/root/var/www/html/index.html') because search permissions are missing on a component of the path

    fix

    run this on the host directory serving the content

    chcon  --user system_u --type httpd_sys_content_t -Rv <dir>

    if you’ve worked with selinux before, you will realise that chcon is a temporary but a faster way to apply contexts to a file. they will be reset in the next relabel. good to use in places where you do not care too much, for example containers.

    if you wish to apply contexts to the file/directory permanently, probably to a directory which is being shared by several containers, file servers, where it doesn’t make much sense to have an extra command to set the security context each time a new container is spun up, then use the following command. you run it one time, and the virtual machines or containers will be able to serve the content correctly.

    semanage fcontext -a -s system_u -t httpd_sys_content_t <dir>

    the above command will make an entry for the file’s context in the /etc/selinux/targeted/contexts/files/file_contexts.local file, which is used to relabel the files in the future. the above command does not apply the context immediately. you will have to do it manually.

    restorecon -RvF <dir>

    reason

    selinux needs the correct context to serve the content

    courtesy –

    https://superuser.com/questions/882594/permission-denied-because-search-permissions-are-missing-on-a-component-of-the-p

    https://unix.stackexchange.com/questions/297701/how-to-label-a-newly-created-file-with-system-u

  • setup and use nfs server on rhel 8

    default nfs version in rhel 8 is version 4

    install nfs-server

    dnf -y install nfs-server nfs-utils

    most probably the nfs-utils package is there on your server already.

    ensure nfs server starts up automatically

    systemctl enable --now nfs-server

    firewall stuff

    firewall-cmd --add-service=nfs --add-service=rpc-bind --add-servicemountd --permanent
    firewall-cmd --reload

    add directories to share on the nfs server

    file controlling the exports is /etc/exports

    check out the man page for exports for more details

    man exports

    example content for /etc/exports file (pasted from the exports man page)

    EXAMPLE
    # sample /etc/exports file
    /               master(rw) trusty(rw,no_root_squash)
    /projects       proj*.local.domain(rw)
    /usr            *.local.domain(ro) @trusted(rw)
    /home/joe       pc001(rw,all_squash,anonuid=150,anongid=100)
    /pub            *(ro,insecure,all_squash)
    /srv/www        -sync,rw server @trusted @external(ro)
    /foo            2001:db8:9:e54::/64(rw) 192.0.2.0/24(rw)
    /build          buildhost[0-9].local.domain(rw)
     
    
    The first line exports the entire filesystem to machines master and trusty.  In addition to write access, all uid squashing is turned off for host trusty. The second and third entry show examples for wildcard hostnames and netgroups (this is the entry `@trusted'). The fourth line shows  the  entry  for the PC/NFS client discussed above. Line 5 exports the public FTP directory to every host in the world, executing all requests under the nobody account. The insecure option in this entry also allows clients with NFS implementations that don't use a reserved port for NFS.  The sixth line exports a directory read-write to the machine 'server' as well as the `@trusted' netgroup, and read-only to netgroup `@external', all three mounts with the `sync' option enabled. The seventh line exports a directory to both an IPv6 and an IPv4 subnet. The eighth line demonstrates a character class wildcard match.

    mount nfs shared directories on your machine

    you’ve got 2 options – root mount, and directory mount.

    root mount – if you mount the / of the nfs server, then all the shared directories with you will appear in this mount.

    otherwise you may check what directories are shared with you using:

    showmount --exports <server_address>

    now mount them individually using the mount command

    notes for adding an entry in the fstab

    version may be specified using the nfsvers= argument

    important – remember to add the _netdev to the options to mount the nfs share after the networking has started on the machine, else…

    example /etc/fstab entry for a nfs share

    nfshost:/   /nfs-share   nfs   defaults,_netdev   0 0

    resolving permissions issue while using nfs

    try chown‘ing the nfs shared directories to nobody

    monitoring nfs server

    nfsstat and nfsiostat

  • awk tricks

    some of the awk tricks listed here. might come in handy in any of my future shell scripts.

    (more…)